Least Privilege: What It is and Why It Improves Corporate Cybersecurity
[INDEX]
- What is the Least Privilege principle and how does it work?
- Why Least Privilege improves corporate cybersecurity
- How to implement Least Privilege in the company
- Examples of applying Least Privilege in the company
- What mistakes should be avoided in privilege management?
- Yookey and the Least Privilege principle
What is the Least Privilege principle and how does it work?
The Least Privilege Principle (PoLP), also known as the principle of minimum privilege, is a cybersecurity model based on the limitation of permissions. It provides that each user, application, process or device is assigned exclusively the permissions necessary to perform the activities within their area of responsibility, avoiding unnecessary access and limiting its validity to the period in which it is actually required.
This approach is based on the Default Deny criterion, according to which access to systems and resources is denied in the absence of explicit authorization. Permissions are therefore granted selectively, based on defined operational requirements.
The application of Least Privilege involves the entire authorization lifecycle, divided into four phases:
- Provisioning: initial assignment of the strictly necessary privileges according to the role and the activities to be performed.
- Usage: application of access limits during normal work activities, ensuring that each user operates exclusively on authorized resources.
- Access Review: periodic checks and audits to verify that the assigned permissions are still appropriate.
- Deprovisioning: removal or revocation of authorizations when they are no longer necessary, for example following a change of duties or the termination of the employment relationship.
Why Least Privilege improves corporate cybersecurity
Applying the principle of minimum privilege means reducing the possibility that a compromised access account could turn into a threat to the entire corporate infrastructure. By limiting the available authorizations, in fact, the attack surface is reduced and the so-called Blast Radius is contained, that is, the extent of the damage that may result from a breach.
If an attacker manages to obtain a user’s credentials with limited privileges, their ability to act remains restricted to the resources accessible through that account. It therefore becomes more difficult to reach critical systems, move laterally within the network or obtain higher authorizations through Privilege Escalation attacks.
Least Privilege also helps counter threats originating from within the organization, both intentional, as in the case of malicious employees, and accidental, due to human errors or improper use of resources. Limiting privileges also represents a containment measure against the spread of malware and ransomware.
A further advantage concerns compliance with the security and data protection requirements established by regulations and reference standards, including GDPR, PCI DSS, HIPAA, NIST, NIS2 and ISO 27001. Controlled management of authorizations makes it possible, in fact, to demonstrate greater attention to information protection and access limitation.
How to implement Least Privilege in the company
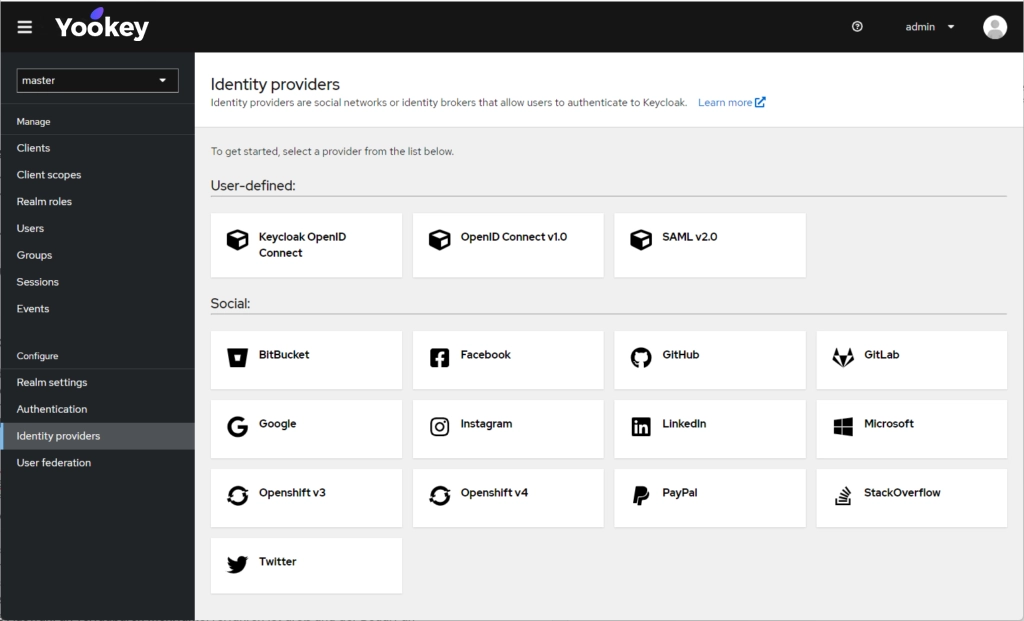
Introducing Least Privilege requires structured management of digital identities and their related authorizations. The first step consists of adopting an Identity Provider (IdP) and defining permission assignment criteria consistent with users’ responsibilities.
For this purpose, access control models such as the following can be used:
- RBAC (Role-Based Access Control): authorizations are assigned based on the role held by the user within the organization.
- ABAC (Attribute-Based Access Control): access to resources is determined by considering specific attributes, such as role, department, device or operational context.
These models should be complemented by the principle of Separation of Duties, which prevents incompatible authorizations from being concentrated in the hands of a single user, reducing the risk of abuse and errors.
Another important element is represented by Privileged Access Management (PAM) solutions, which make it possible to control and protect accounts with elevated privileges. Through Just-In-Time (JIT) mechanisms, administrative authorizations can be granted exclusively when needed, for a limited period of time and with automatic revocation at the end of the activity.
The implementation of Least Privilege must also consider the security of the devices used to access corporate resources. Continuous assessment of their level of reliability and the adoption of Zero Trust Network Access (ZTNA) technologies, as an alternative to traditional VPNs, make it possible to apply more granular controls to connections between users and applications.
Finally, to keep the model effective over time, it is necessary to provide for periodic authorization checks, automated access recertification processes and timely deprovisioning procedures.
Ready-Made Templates
Are you looking for an IAM System?Visit the Yookey website to discover the available solutions.
Examples of applying Least Privilege in the company
The principle of minimum privilege is applied in numerous business activities and can be adopted both for user accounts and for automated applications and services. Some practical examples help to understand how it works:
- Separation between standard and administrative accounts: during normal work activities, an employee uses an account without administrative privileges, which does not allow, for example, installing software or modifying system configurations. Root or admin accounts are instead reserved for operations that actually require elevated authorizations.
- Limiting access to data and information: a technical support operator or a financial analyst can consult the logs and information necessary to perform their work, without automatically having access to production databases or all corporate financial documents.
- Permission control in development environments: a developer may be authorized to upload and modify code within a repository, without having the permissions necessary to directly deploy it to the production environment.
- Authorizations for automated services and processes: accounts used by applications and services must also comply with the principle of minimum privilege. For example, an automatic backup system may have read-only permissions to copy data, without being able to modify or delete it.
What mistakes should be avoided in privilege management?
The effectiveness of Least Privilege depends on the ability to keep authorizations under control over time. Some incorrect practices can compromise its application, creating vulnerabilities and leaving users or services with more permissions than are actually necessary.
Among the most common mistakes are:
- Privilege Creep: consists of the progressive accumulation of authorizations that are no longer necessary. This can occur when an employee changes role, department or duties, or completes a project, without the previously assigned privileges being updated or revoked.
- Granting excessive privileges for convenience: assigning permanent administrative authorizations to speed up daily activities is a risky practice. Service accounts should also have only the essential permissions, avoiding unjustified elevated privileges.
- Lack of control over non-human accounts (NHI): service accounts, bots and API keys are sometimes overlooked in identity management processes. Leaving them with elevated authorizations, permanent credentials and without adequate rotation procedures increases the risk of compromise.
- Excessive rigidity of authorization processes: approval procedures that are too slow or complex can hinder employees’ work, pushing them to use unauthorized tools and applications. This phenomenon, known as Shadow IT, can also extend to the uncontrolled use of artificial intelligence tools, giving rise to the so-called Shadow AI.
- Absence of audits and incomplete offboarding procedures: failing to periodically check assigned privileges and not promptly deactivating the accounts of employees who leave the organization means keeping potentially dangerous access accounts active.
Yookey and the Least Privilege principle
To concretely apply the principle of minimum privilege, it is essential to have tools that make it possible to centralize identity management and control authorizations throughout their entire lifecycle.
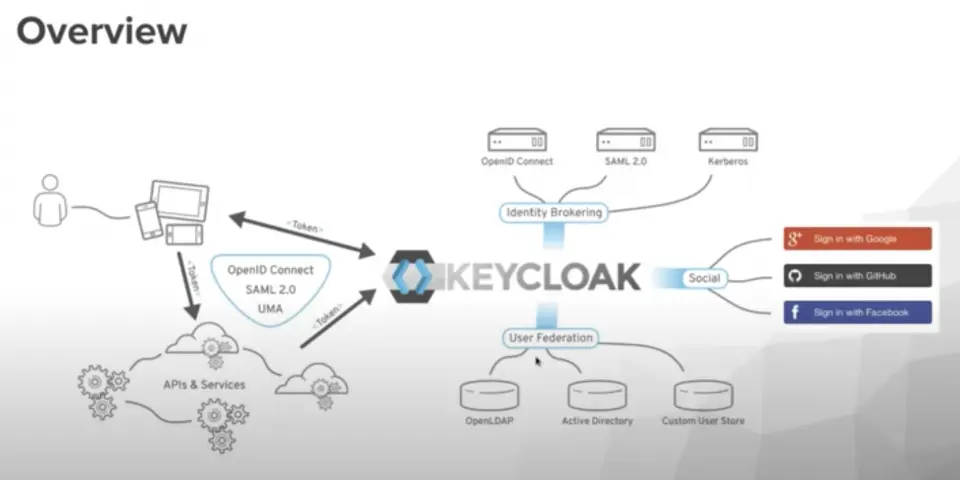
Yookey is a fully managed SaaS IAM service based on Keycloak, which allows companies to centralize and simplify access management for applications. The platform provides secure authentication systems through Single Sign-On (SSO) and Multi-Factor Authentication (MFA), also supporting Passkeys, SPID and CIE.
Thanks to its native integration with YooPoint, Identity Governance and Administration (IGA) software, Yookey makes it possible to manage the entire lifecycle of digital identities in a coordinated way. From onboarding new users to managing role changes, through to offboarding, it is possible to govern the assignment, modification and revocation of roles and authorizations through granular and automated processes.
Speak directly with our team to learn more