Keycloak 26.8: the 5 main new features of the latest Version
[INDEX]
- Automatic User and Group Provisioning via SCIM APIs (Supported)
- Simplified Multi-Cluster Management with Stateless Architecture (Supported)
- Token Exchange and Access Delegation for AI Agents and External Applications (Preview)
- Verifiable Digital Credentials: New Features for the OID4VCI and OID4VP Standards
- Greater Reliability in Brute-Force Attack Protection and SAML SLO Fix in Keycloak 26.8.1
- Yookey: the IAM Solution Based on Keycloak with SPID and CIE

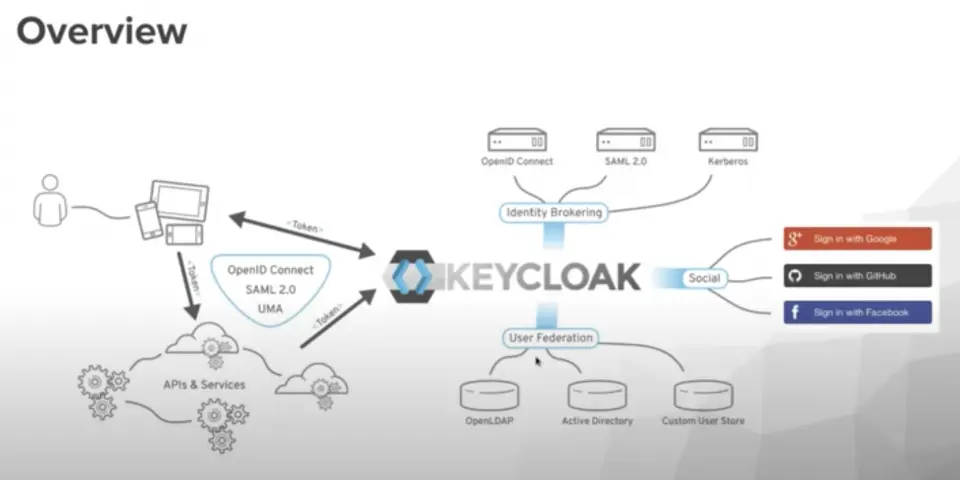
The Keycloak 26.8 release introduces significant improvements in digital identity and access management (IAM, Identity and Access Management). The new features mainly concern the evolution of the architecture for cloud-native environments, the integration of open standards for user provisioning and verifiable credentials, as well as new security features designed to support increasingly complex use cases, including those involving artificial intelligence agents.
Here are the 5 main new features in Keycloak 26.8 and their implications for identity management, automation and access protection.
1. Automatic User and Group Provisioning via SCIM APIs (Supported)
With Keycloak 26.8, support for the SCIM (System for Cross-domain Identity Management) standard for user and group management becomes officially available.
This functionality makes it possible to automate identity synchronization between Keycloak and external systems, such as HR platforms and Identity Governance solutions. It is therefore possible to manage user account creation, updates and deactivation centrally and automatically.
2. Simplified Multi-Cluster Management with Stateless Architecture (Supported)
The new stateless mode (–features=stateless) is introduced as an officially supported feature and allows multiple Keycloak clusters to be connected using the database to persist sessions.
This approach reduces infrastructure complexity by eliminating the need to configure cross-site replication of an external Infinispan instance. At the same time, the previous multi-cluster v1 architecture is deprecated, promoting a deployment model that is easier to manage.
Ready-Made Templates
Looking for an IAM or IGA platform to manage digital identities?Visit the Yookey website to discover the available solutions.
3. Token Exchange and Access Delegation for AI Agents and External Applications (Preview)
Keycloak 26.8 introduces preview functionality for access delegation through the parameterized scope delegation:client:. This mechanism allows users to authorize AI agents and third-party applications to access permitted resources through an OAuth-based consent flow.
The issued tokens include the act claim, which identifies the delegation context. The feature also includes an explicit restriction: delegated tokens cannot be used to access Keycloak Admin APIs. This restriction helps prevent privilege escalation and maintain a separation between user permissions and those of delegated applications.
4. Verifiable Digital Credentials: New Features for the OID4VCI and OID4VP Standards
The release expands support for verifiable digital credentials by introducing preview functionality based on the OpenID for Verifiable Credential Issuance (OID4VCI) standard. The update makes it possible to manage the credential lifecycle, including revocation mechanisms integrated with refresh tokens and key attestation capabilities.
These new features are complemented by experimental support for verifying credentials presented through digital wallets during authentication processes, based on the OpenID for Verifiable Presentations (OID4VP) standard. This development expands Keycloak’s integration possibilities with digital identity systems based on verifiable credentials.
5. Greater Reliability in Brute-Force Attack Protection and SAML SLO Fix in Keycloak 26.8.1
Among the security improvements, Keycloak 26.8 introduces database persistence for data relating to lockouts resulting from repeated failed authentication attempts. This setting, enabled by default, makes it possible to retain lockout information even after cluster nodes restart, preventing the protection state from being lost due to a service interruption.
The Keycloak 26.8.1 patch also includes a security fix related to the SAML Single Logout (SLO) protocol. The fix prevents a client from improperly terminating sessions associated with other applications, strengthening isolation between different authentication contexts and improving the overall security of session management.
Yookey: the IAM Solution Based on Keycloak with SPID and CIE
Yookey is an Identity and Access Management (IAM) solution based on Keycloak that ensures robust and secure management of digital identities and access control to resources and services.
The solution simplifies and secures onboarding and offboarding processes through integration with Single Sign-On (SSO) and advanced access management automation, while applying multi-factor authentication (MFA) mechanisms to strengthen security from the very first login.
Yookey integrates natively with YooPoint, the IGA (Identity Governance and Administration) software within the E-time Suite, enabling the management of the entire digital identity lifecycle.
Speak directly with our team for more information.